This user has not added any information to their profile yet.
"Fredrik has an uncanny ability to communicate to both C Suite and Technical resources, more importantly, bridge that gap."
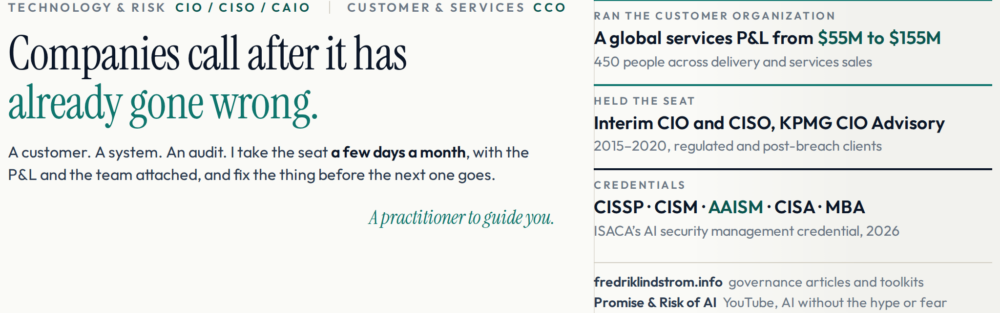
What I bring to a fractional seat: AI delivering real business value; an AI governance position with a named owner and halt authority instead of a policy document; a control environment an examiner will accept; or a services operating model that holds its margin. CISSP, CISM, CISA, AAISM.
Four AI systems running in production, not pilots. One writes the statement of work from the customer call transcript, removing a scoping step that sat between sale and delivery. Another scans roughly 20,000 opportunities a month for work that was never scoped or never attached. I architected and launched an AI security practice that delivered 100+ engagements and about $4M in its first six months, and gave account teams the lever that won back a $25M bank relationship on its way out the door — while taking administrative load off a 42-person team rather than adding to it.
Most fractional executives have run something big or something small. I have done both. At Check Point I scaled services from $55M to $165M and built managed security from zero to more than $80M in three years. Earlier I grew a security practice from 6 engineers to 40, and another from 3 to 20. Since 2020 I have held a part-time CISO seat at a six-person regulated firm, where nothing gets absorbed by a team, because there is no team.
The hard part of a fractional seat is subtraction. Knowing which nine things to leave out so the one that matters gets done.
CISSP (ISC2) · CISM (ISACA) · CISA (ISACA) · AAISM — ISACA Advanced in AI Security Management · PMP (PMI) · ITIL
Vendor: AWS Advanced Networking Specialty · VMware VCP-NV · Check Point Master Architect (CCMA) · Cisco CCNP/CCDP · Juniper JNCIP-ENT
Memberships: ISC2, ISACA, PMI
Board: Advisory Board Member (non-executive), UK AI startup — Aug 2026 to present
MBA, Rollins College Crummer Graduate School of Business · B.Sc. Computer Science, KTH Royal Institute of Technology, Stockholm
A financial-services firm entered bankruptcy reconstruction and a divestiture at the same time. I came in as interim CIO with full accountability for the entire IT and cybersecurity estate — infrastructure, applications, business systems, end-user services and security.
The estate was built for a company that no longer existed: 300 people and three datacentres against a cost base of roughly $115M. Every decision had to survive a creditor committee and a buyer's diligence at once, so nothing could be done on a promise of future savings.
We took IT to 50 people and a single colocation facility and removed about 80% of the IT cost base, while keeping the business running through the sale. Not a technology problem — a sequencing one. What to cut first, what to keep alive until the deal closed, and what the buyer needed to still be standing on day one.
I have done the same shape twice more: interim CISO for six months at a private-equity firm, building the documentation they had never had and handing a working baseline to the permanent hire; and six years part-time as CISO of a small regulated firm, where the constraint is not budget but attention.
Grew services revenue $55M → $165M; professional services 150 → 450+ people across 75+ countries
Built managed security services from $0 → $80M+ in three years
Lifted delivery margin ~22 points by converting 100% T&M to ~80% fixed-fee outcome-based
Cut ~80% from a ~$115M IT cost base as interim CIO; 300 people → 50, three datacentres → one
Moved net revenue retention +17 points through services attach (93 → 110+)
AI security practice: 100+ engagements and ~$4M in its first six months
My M&A work is diligence and integration — the part after the term sheet.
I managed technical integration for the $600M Accuvant/Optiv merger, unifying delivery, training and customer engagement across two organisations that had been competing the week before.
At Check Point I ran technical due diligence on a $20M managed-services acquisition, then the integration: IP, team and tooling onto one platform with no disruption to live customers.
The other direction too. As interim CIO through a bankruptcy reconstruction and divestiture, I owned the IT and security estate through the sale — what to cut, what to keep alive until close, what the buyer needed standing on day one.
And at the size most firms actually buy at: the technology and data side of two practice acquisitions at a regulated accounting firm, $115K and $150K.
United States, Sweden, UKI, Australia, Singapore, Hong Kong, Philippines, Italy, Spain, Germany, Switzerland, Israel, UAE.